Education project
Cybersecurity Labs
From reconnaissance to controls, in controlled environments
Three lab reports from the diploma, from reconnaissance with Nmap to privilege escalation, and the analysis of a cyberattack with its response plan.
What it is about
Politécnico's cybersecurity diploma, from September to December 2026, is assessed through lab reports. Each one documents a controlled, authorized environment, what was done step by step and the controls that would have prevented it.
The reports are in Markdown, Word and PDF, with Mermaid diagrams and numbered screenshots of every step.
What it does
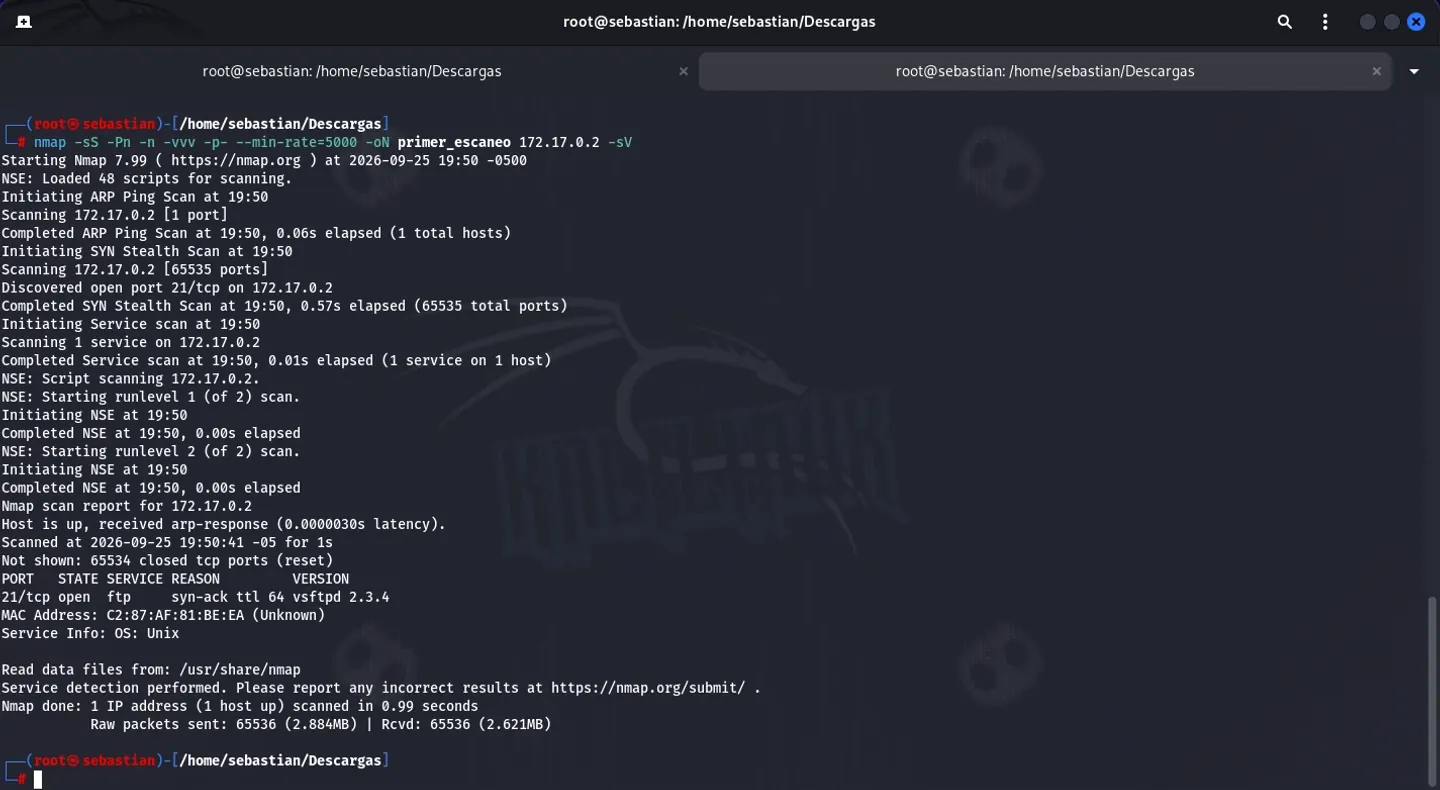
- Lab 1: reconnaissance of a vulnerable machine on an isolated Docker network, with Nmap scans from less to more detail until vsftpd 2.3.4 shows up, and research into its backdoor.
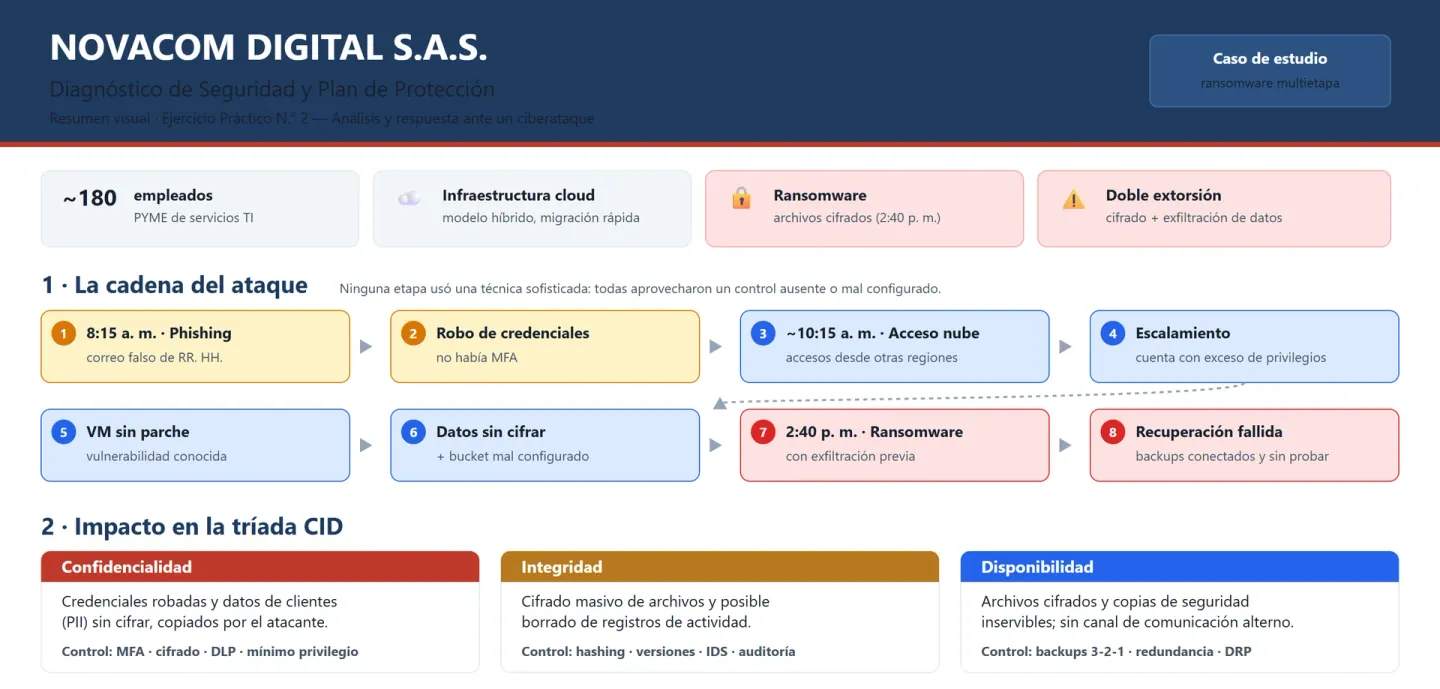
- Lab 2: the analysis of a phishing attack that ends in double-extortion ransomware, its threats and vulnerabilities, the confidentiality, integrity and availability principles, a role-based access control matrix and a secure cloud architecture.
- Lab 3: a complete CTF, from reconnaissance and an information leak to authorized brute force with Hydra and privilege escalation, plus a controlled availability test on WordPress with ApacheBench and wrk.
- Controls aligned with ISO/IEC 27001, the NIST CSF and the SP 800-61 and SP 800-34 guides, and with Colombia's data protection law.
- Each report documents its safety conditions, its environment and its evidence with numbered screenshots; the third one verifies its outputs with SHA-256.
How it works
The three labs
Each lab moves from reconnaissance or analysis to defensive controls.
Lab 1
- Reconnaissance with Nmap
- vsftpd 2.3.4 and its backdoor
- Isolated network and safety rules
Lab 2
- Phishing and ransomware case
- Confidentiality, integrity and availability
- Role-based access control and a secure cloud
Lab 3
- CTF from reconnaissance to initial access
- Privilege escalation
- Controlled availability test
Decisions and their costs
Authorized environments only
Every lab applies attack techniques, and they can only run where there is authorization.
Repositories
Every public repository of the project, with what it holds.
- 2026Kali Linux, Nmap, Hydra, Docker
CybersecurityEngineeringSebastian-s
Lab reports of the cybersecurity diploma, with the vulnerability analysis of an FTP service, a CTF up to privilege escalation and the response to a cyberattack case.
Stack
Pick a technology to see the projects that use it.